I am a security-focused technologist with a deep curiosity for understanding how protocols break and how
defensive architectures withstand modern adversaries. Rather than viewing security as an afterthought, I
approach engineering with a security-first, zero-trust mindset.
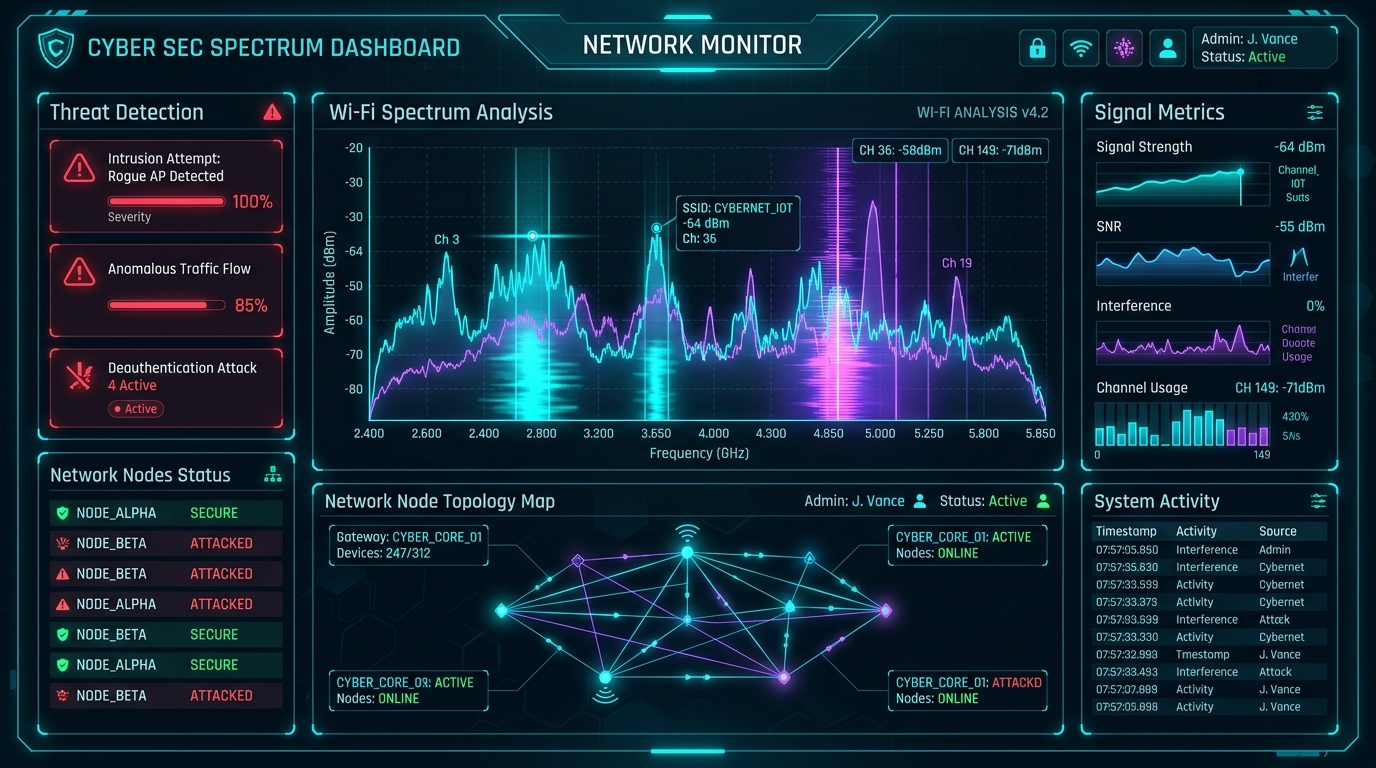
My core technical fascination lies in wireless radio frequency auditing, rogue access point
heuristics, and password entropy thermodynamics. I enjoy dissecting 802.11 spectrum traffic,
understanding the cryptographic nuances of WPA2 vs WPA3-SAE, and developing native operating system tools
that turn passive network reconnaissance into actionable threat scoring.
What I am currently building & learning: Deepening my hands-on practice in memory
forensics, threat hunting with Zeek & Suricata, and building automated security verification pipelines that
combine LLM vector indexing with structured vulnerability feeds.
🛰️
RF & Wireless Auditing
Passive 802.11 netsh hooks, spectrum overlap detection, and rogue AP heuristics.
🔐
Applied Cryptography
Shannon entropy evaluation, pre-shared key resistance, and cipher downgrade
defense.
🧱
Secure Full-Stack Dev
Defending against OWASP Top 10 vulnerabilities, strict RBAC, and input
sanitization.
🧪
Adversary Emulation
Hands-on CTF exploration, lateral movement analysis, and defensive blue-team
hardening.